Tech Support For Dummies

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg

Monday, 9 January 2012

New Year's Resolutions merely create gym overcrowding

Posted on 08:03 by Unknown
Be it New Year's resolutions (I'm going to lose weight this year!), career resolutions (I'm going to get a different job this year!) or financial resolutions (I'm going to get out of debt this year!)....traditional resolutions just don't work.

Just check out how your local gym parking lot transforms between now and next month. I can't wait until around mid-February when the crowds will predictably die down and I can get some personal space back when I'm working out!

We've all fallen into the trap of "resolving" to do something but not following through to actually make it happen. You know what's been said about the road to Hell being paved with good intentions. With resolutions we only end up letting ourselves down and planting those seeds of doubt in our mind that certain tasks can never be accomplished. It's just not true...IF you go about it the right way.

Here's a proven method for doing what you say you're going to do and making stick once and for all in order to enhance your job, your career and your personal life for 2012. It has worked for me and I know you can benefit as well if you make it so.
Read More
Posted in careers, goal setting, personal responsibility, thinking long term | No comments

Thursday, 5 January 2012

My Web app security epiphany: The Lysol Effect

Posted on 08:16 by Unknown
I just had an epiphany in the bathroom. I know, I know...bear with me.

I thought to myself, Why is it people use Lysol to cover up, um, smells and such in the bathroom?? Sure Lysol kills the problem at the source but, goodness gracious, there are other means of consideration than to merely cloud up the bathroom covering up something that probably shouldn't be there in the first place! Know what I mean? Why not take preventive measures to keep things in check rather than junk up the bathroom and surrounding areas with yet another foul scent?

Then it hit me...this social dilemma is no different than people relying solely on Web application firewalls for Web security. We know problems like SQL injection, XSS and session management are there. Why not just fix the flaws rather than covering them up? I wrote about this in a piece on PCI DSS 6.6 compliance four years ago and I still see and hear about this a lot...priorities I suppose.

Anyway....apparently I have an uncanny ability to tie bathroom logic in with information security. It's an awful personality flaw. Please don't hold it against me.
Read More
Posted in application firewalls, humor, message from Kevin, scary stuff, stupid security, thinking long term, web application security, web server security | No comments

Tuesday, 3 January 2012

Great quote to live by

Posted on 16:42 by Unknown
Here's one of my favorite #quotes you can apply to your career, regardless of which field you're in:

"A successful life is one that is lived through understanding and pursuing one's own path, not chasing after the dreams of others." -Chin-Ning Chu
Read More
Posted in careers, great quotes, information security quotes, personal responsibility, security leadership, thinking long term | No comments

Damballa’s Fight Against Advanced Malware

Posted on 11:30 by Unknown
Malware being out of sight and out of mind often creates the perception that risks aren't present. Just because there’s no perceived risk, doesn’t mean it’s not there. Heads buried in the sand over the real malware threat leads to breaches that most organizations aren't prepared to handle. Having worked on a project involving an APT infection, I’ve seen first-hand how ugly this stuff can get.

Endpoint protection isn’t enough. Analyzing executables isn’t enough. Even standalone monitoring of network communications and or rating of source malware sources isn’t enough to thwart the real problem. Like the core information security principle, you’ve got to layer controls if you’re going to get the most out of your malware protection.

One of my core information security principles I recommend to my clients is to use what you’ve got when it makes sense. By this I mean use the built-in security controls that your operating systems, databases, network infrastructure devices and so on already have. So many of us assume that we need to buy third-party products to keep our environment secure. This is not true in so many cases.

However, when it comes to fighting advanced malware, it’ll behoove you to use the niche technologies that specialize in this area. The market is tiny (relatively speaking) but Damballa’s Failsafe is worth checking out. I’ve seen Failsafe 5.0 in action and it seems to be a comprehensive solution to a widespread problem that I suspect is only going to get worse. As you've heard me say regarding Web application scanners, password cracking and the like, you've got to have good tools if you're going to find (and, in this case, control) what matters.

I’ve written a new paper where I talk more about the advanced malware problem and how Damballa Failsafe 5.0 fits into the overall information risk equation. Check it out.
Read More
Posted in cool products, incident response, malware, scary stuff, stupid security | No comments

Monday, 2 January 2012

Let's make 2012 the year we get past "compliance" as we've known it

Posted on 13:09 by Unknown
I hope your 2012 has gotten off to a grand start! Mine has. I believe this year is going to further demonstrate why we're working in one of the best possible fields in the world.

To get things rolling this year, I wanted to share with you a few new pieces I've written for TechTarget's SearchCompliance.com regarding...well, compliance. It's one of those topics that tends to infuriate me when it comes to government intrusion into the free market and our own personal lives. However you see it, compliance is still something you have to address in your business. Hopefully some of these bits will help take some of the pain out of compliance. Enjoy!

Top compliance questions you need to be asking your network administrators

Address information risk management now — before the going gets tough

How can you avoid a Web security breach? It's all in the preparation.

Seven dangerous assumptions about compliance

A thorough data retention strategy needs more than just IT oversight

Top 5 techniques for management buy-in for your IT governance strategy

As always, be sure to check out www.principlelogic.com/resources.html for links to all of my information security whitepapers, podcasts, webcasts, books and more.
Read More
Posted in compliance, data breaches, data retention, hacking, Kevin's security content, message from Kevin, risk management, security policies, web application security | No comments

Tuesday, 20 December 2011

Holiday wishes and what's in store for 2012

Posted on 12:06 by Unknown
I'd like to send out a special holiday wish to everyone: Merry Christmas, Happy Hanukkah and Happy New Year!

This year has been extraordinarily great for me in my business and I owe it all to my clients, presentation and seminar participants, and purchasers of my books and audio content. Thank you very much!

I have lots of neat things right around the corner including a YouTube video channel and new Security On Wheels audio programs. In fact, I've already started on my videos and am pulling together some fresh audio content based on the feedback I've gotten regarding my presentations, seminars and webcasts over the past year.

It's time for me to disconnect for a couple of weeks. Here's to a great 2011 and an ever greater 2012!

All the best,
Kevin
Read More
Posted in audio programs, Kevin's seminars, Kevin's videos, message from Kevin | No comments

Saturday, 17 December 2011

WebInspect: How SQL injection testing *should* be done

Posted on 12:56 by Unknown
SQL injection is arguably the grandest of all security vulnerabilities. It can be exploited anonymously over the Internet to gain full access to sensitive information - and no one will ever know it occurred. Yet time and again it's either:
  1. overlooked by people who don't test all of their critical systems from every possible angle
  2. overlooked by people who haven't learned how to properly use their Web vulnerability scanners
  3. overlooked by people who chose to only perform PCI-DSS-type vulnerability scans that don't go deeply enough
  4. And, perhaps worst of all, overlooked by tools that can't test for - or properly exploit - SQL injection

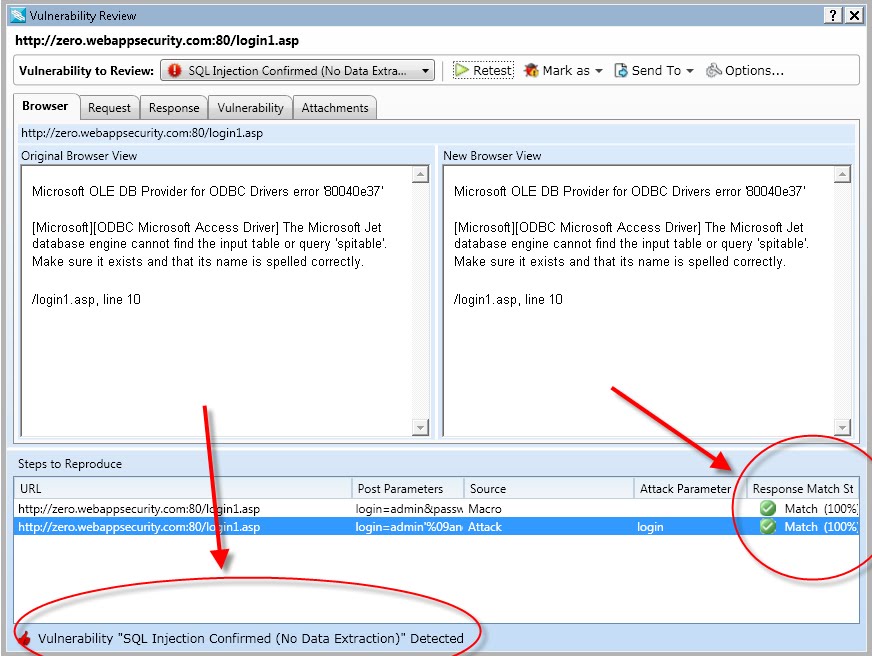
Certain automated tools for SQL injection testing/exploitation have been around for years but I've never seen a tool that actually finds SQL injection as frequently or is as simple to use as HP's WebInspect. As shown in the following screenshots, with WebInspect it's a simple two-step process from initial scan to data extraction:

Step 1: Run the vulnerability scan to find SQL injection flaws. Finding it is half the battle. Most vulnerability scanners have no clue of its existence.


Step 2: Right-click on the finding, load the SQL Injector tool to confirm the injection and then click Pump Data to automatically siphon data out. Yes, it's that simple. (Note: in this test instance, extraction was not possible but it is in at least half of the SQL injection flaws I come across).


At your option, you can also use WebInspect's Vulnerability Review function to go back and test the SQL injection flaws once a fix is put in place...no need for a full rescan. Love it.


Folks, this is something that cannot be taken lightly. I'm not just talking about SQL injection itself but the fact that your tools may not be providing you the right information you need. As I've said before, You cannot secure what you don't acknowledge. In this case, I'll tweak that a bit and say You cannot secure what you cannot find. Just because the tools you're using aren't finding or exploiting SQL injection doesn't mean it's not a problem. Trust but verify.
Read More
Posted in automated scanner oversights, cool products, penetration testing, SQL injection, vulnerability assessments, web application security, WebInspect | No comments
Newer Posts Older Posts Home
Subscribe to: Posts (Atom)

Popular Posts

  • Reaver Pro: a simple tool for cracking WPA on a LOT of wireless networks
    If wireless security testing is on your radar, you need to get Reaver Pro . As I outlined in this Hacking For Dummies, 4th edition chapter ,...
  • Low information users and the challenges they create
    Thanks to the political elite and the dumb masses they inspire, you've probably heard the term low information voter …In a nutshell, thi...
  • "Top Blogs" list & some home security considerations
    I think I may have found the first sign that my blog is growing and gaining some traction. I've made it to the Top 20 Home Security Blog...
  • Wooo...HIPAA audits are coming & the irony of KPMG's involvement
    I've always believed that compliance is a threat to business [hence why I help businesses take the pain out of compliance by addressing ...
  • Windows 8.1 changes/enhancements, BitLocker's improvements, and related Windows mobile/security tips
    In addition to my independent information security assessments through my consultancy Principle Logic , I've been writing a ton...includ...
  • What you need to know about security vulnerability assessments (that no one is willing to share)
    I'd love it if you'd join me over at SearchSecurity.com next week where I'll be talking about the rest of the story regarding ...
  • Sprechen Sie Deutsch? Hacking For Dummies now in German!
    Check out the latest foreign-language edition of my book Hacking For Dummies: Hacking For Dummies is now in 6 languages: English, Estonian, ...
  • It's hard being human
    Cavett Robert once said something about character that resonates within information security - especially regarding ongoing management and l...
  • Experiencing problems with authenticated web vulnerability scans? Try NTOSpider.
    You're performing authenticated web vulnerability scans , right? If you're not, you're missing out...big time. When performing a...
  • The compliance crutch mentality rides on
    I believe it was my colleague Kevin Bocek who once said: "Security done right will yield compliance for free. Compliance for complianc...

Categories

  • active directory
  • application firewalls
  • APTs
  • aslr
  • atm security
  • audio programs
  • audit logging
  • automated scanner oversights
  • back to basics
  • backups
  • big brother
  • bitlocker
  • budget
  • business case for security
  • business continuity
  • BYOD
  • car hacking
  • careers
  • certifications
  • change management
  • checklist audits
  • cissp
  • clear wireless
  • cloud computing
  • communication
  • compliance
  • computer glitch
  • conferences
  • consulting
  • content filtering
  • cool products
  • cool sites
  • cross-site request forgery
  • cross-site scripting
  • csrf
  • customer no service
  • cybersecurity bill
  • data at rest
  • data breach laws
  • data breaches
  • data centers
  • data destruction
  • data leakage
  • data protection
  • data retention
  • database security
  • degrees
  • desktop management
  • disaster recovery
  • disk imaging
  • disposal
  • dns
  • document security
  • domino
  • DoS attacks
  • drive encryption
  • e-discovery
  • ediscovery
  • employee monitoring
  • encrypting data in transit
  • encryption
  • end point security
  • ethical hacking
  • exchange
  • experience
  • expert witness
  • exploits
  • facebook
  • FERPA
  • file integrity monitoring
  • firewalls
  • forensics
  • full disk encryption
  • global warming
  • goal setting
  • good blogs
  • government intrusion
  • government regulations
  • great quotes
  • hacking
  • hardware
  • hipaa
  • hitech
  • hitech act
  • home security
  • humor
  • identity access management
  • identity theft
  • IIS
  • incident response
  • information classification
  • information security quotes
  • intel
  • intellectual property
  • internal threat
  • java
  • Kevin's books
  • Kevin's interviews
  • Kevin's keynotes
  • kevin's panels
  • kevin's quotes
  • Kevin's security content
  • Kevin's seminars
  • Kevin's videos
  • laptop encryption
  • laptop security
  • legal
  • Linux
  • locking screens
  • low-hanging fruit
  • malware
  • marketing hype
  • message from Kevin
  • messaging security
  • metasploit
  • metrics
  • mobile apps
  • mobile security
  • motivation
  • multi-factor authentication
  • network analysis
  • network complexities
  • network protocols
  • network security
  • networking essentials
  • Novell
  • office
  • online backup
  • online safety
  • open source security
  • owasp
  • p2p
  • passwords
  • patch management
  • patching
  • pci 6.6
  • pci dss
  • PCNAA
  • penetration testing
  • people problems
  • personal responsibility
  • phishing
  • physical security
  • pii
  • podcasts
  • policy enforcement
  • politics
  • presentations
  • privacy
  • quality assurance
  • recommended books
  • recommended magazines
  • recycling
  • remote access security
  • ridiculous password requirements
  • risk analysis
  • risk management
  • rogue insiders
  • ROI
  • RSA 2012
  • running a business
  • saas
  • salary
  • scary stuff
  • sccm
  • sdlc
  • security assessments
  • security audits
  • security awareness
  • security committees
  • security leadership
  • security management
  • security operations
  • security policies
  • security policy
  • security scans
  • security standards
  • security statistics
  • security technologies
  • security testing tools
  • security tools
  • selling security
  • sharepoint
  • small business
  • smartphone security
  • SMBs
  • social media
  • software development
  • source code
  • source code analysis
  • special offer
  • SQL injection
  • sql server
  • ssl
  • storage security
  • student information systems
  • stupid security
  • success
  • telecommuting
  • testimonials
  • thinking long term
  • third-party applications
  • threat modeling
  • time management
  • training
  • twitter
  • uncool products
  • unstructured information
  • unstructured infromation
  • user awareness
  • vendors
  • virtual machine security
  • visibility
  • voip
  • vulnerability assessments
  • web 2.0
  • web application security
  • web browser security
  • web server security
  • webcasts
  • WebInspect
  • whitelisting
  • whitepapers
  • Windows
  • Windows 7
  • windows 8
  • windows 8.1
  • Windows Mobile
  • windows security
  • Windows Vista
  • wireless
  • wireless security
  • zero tolerance

Blog Archive

  • ▼  2013 (35)
    • ▼  November (3)
      • Reaver Pro: a simple tool for cracking WPA on a LO...
      • Low information users and the challenges they create
      • My latest security content (lots of stuff on appli...
    • ►  October (3)
    • ►  September (1)
    • ►  August (2)
    • ►  July (3)
    • ►  June (1)
    • ►  May (4)
    • ►  April (4)
    • ►  March (4)
    • ►  February (5)
    • ►  January (5)
  • ►  2012 (77)
    • ►  December (2)
    • ►  November (2)
    • ►  October (4)
    • ►  September (3)
    • ►  August (3)
    • ►  July (4)
    • ►  June (5)
    • ►  May (9)
    • ►  April (5)
    • ►  March (10)
    • ►  February (14)
    • ►  January (16)
  • ►  2011 (163)
    • ►  December (15)
    • ►  November (11)
    • ►  October (9)
    • ►  September (16)
    • ►  August (13)
    • ►  July (8)
    • ►  June (13)
    • ►  May (18)
    • ►  April (16)
    • ►  March (13)
    • ►  February (13)
    • ►  January (18)
  • ►  2010 (170)
    • ►  December (10)
    • ►  November (14)
    • ►  October (7)
    • ►  September (27)
    • ►  August (20)
    • ►  July (8)
    • ►  June (15)
    • ►  May (4)
    • ►  April (23)
    • ►  March (21)
    • ►  February (11)
    • ►  January (10)
  • ►  2009 (55)
    • ►  December (5)
    • ►  November (10)
    • ►  October (21)
    • ►  September (19)
Powered by Blogger.

About Me

Unknown
View my complete profile