Tech Support For Dummies

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg

Wednesday, 13 November 2013

Reaver Pro: a simple tool for cracking WPA on a LOT of wireless networks

Posted on 13:47 by Unknown
If wireless security testing is on your radar, you need to get Reaver Pro. As I outlined in this Hacking For Dummies, 4th edition chapter, Reaver Pro is a great tool for cracking the WPA pre-shared key on all those consumer-grade wireless APs/routers that everyone installs in the enterprise.

The latest version of Reaver Pro is very simple to use. No live CDs or VMs to boot. You simply connect the device into your test system's Ethernet port, connect the power adapter, browse to 10.9.8.1, login, and you're ready to roll. Here is a quick video overview and here is a screenshot showing its interface:


Terry Dunlap with Tactical Network Solutions (the company that created and sells Reaver Pro) has a great team of sharp guys...and they've been very responsive when prompted with my mostly dumb questions.

If anything let Reaver Pro be a reminder of two things:
  1. WPA is a proven wireless security control that's only as good as the weakest link on your network
  2. Consumer grade wireless APs and routers don't have a place in a business setting - although on practically every network I see.
It seems to me that with the advent of WPA, WPA2, and enterprise-grade wireless security controls that people have let their guard down a bit with wireless security.

Don't be that guy.

As I like to say, you can't secure what you don't acknowledge! WPS is enabled by default in most situations. It's broken. Even if you have the option to throttle PIN requests, you need to find WPS and disable it (even on your home wireless). The convenience factor it provides is just not worth the risk of someone gaining full access to your wireless (and likely wired) network.
Read More
Posted in cool products, encrypting data in transit, Kevin's books, penetration testing, security testing tools, vulnerability assessments, wireless security | No comments

Tuesday, 12 November 2013

Low information users and the challenges they create

Posted on 08:25 by Unknown
Thanks to the political elite and the dumb masses they inspire, you've probably heard the term low information voter…In a nutshell, this term refers to people making a critical decision without knowing all the facts.  As Winston Churchill once said “The best case against Democracy is a five minute conversation with the average voter.”

Interestingly, this concept and quote make me think of information security and why we need to prepare ourselves for today’s threats. Have a five minute conversation with an average user on your network. Talk to them about what they do and don’t do, the decisions that they’re making regarding their computer usage, and so on and it will likely become clear that we have a problem that we must solve.

If you're looking for answers to this human psychology challenge, here is a piece I wrote with tips for getting (and keeping) users on your side with IT and security.

Check out a related piece I wrote for Rapid7's blog:
Why business execs know more about security than you do

Best of luck! Keep in mind that sticktuitiveness is the key to all of this.


Read More
Posted in careers, scary stuff, security leadership, selling security, stupid security, thinking long term | No comments

Monday, 11 November 2013

My latest security content (lots of stuff on application security)

Posted on 14:02 by Unknown
I thought you might be interested in my latest articles/tips on web and mobile application security:

Why you need to pay attention to the slow HTTP attack

Lessons learned from a web security breach

Application security calls for a proactive approach

Understanding the value of the OWASP Top 10 2013

The Role Of An Automated Web Vulnerability Scanner In A Holistic Web Security Audit

Are Obamacare’s health insurance exchanges secured? Likely not.

Can software quality pros shore up network security threats?

How do software quality pros navigate cloud computing security issues?

What are the hidden mobile app security threats to look out for?

Also, be sure to check out principlelogic.com/resources for links to hundreds of additional security resources I've written and developed over the past 12 years.
Read More
Posted in cloud computing, data breaches, DoS attacks, incident response, Kevin's security content, mobile apps, security standards, software development, vulnerability assessments, web application security | No comments

Friday, 18 October 2013

What you need to know about security vulnerability assessments (that no one is willing to share)

Posted on 07:37 by Unknown
I'd love it if you'd join me over at SearchSecurity.com next week where I'll be talking about the rest of the story regarding security assessments...

You know the tools and you're probably familiar with the methodologies...that's why I'm going to share with you many other important aspects of security assessments that, unless someone tells you, you'll likely only learn the hard way. And that's no fun.

In my webcast What you need to know about security vulnerability assessments (that no one is willing to share), I'll outline what to do, what not to do, and what you can expect to get out of your vulnerability assessments (or pen tests, or audits, or whatever you call them).

These are things that I've learned in over a decade and a half performing security assessments for hundreds of organizations, thousands of websites/applications/mobile apps, and tens of thousands of network hosts. And there's no cost to you.

Areas I'll cover are the essence of my book Hacking For Dummies including:  
  • Glaring flaws you’re overlooking today
  • Mistakes you're making...and cannot afford
  • Approaches that are guaranteed to help you find the most holes
  • Scoping your next round of testing to maximize its value and minimize your effort
Attendees will be included in a drawing for one of several signed copies of the new 2013 (4th) edition of Hacking For Dummies.


You can register here. Hope to see you next week!
Read More
Posted in Kevin's books, Kevin's security content, message from Kevin, penetration testing, security assessments, security audits, vulnerability assessments, webcasts | No comments

Tuesday, 8 October 2013

Windows 8.1 changes/enhancements, BitLocker's improvements, and related Windows mobile/security tips

Posted on 02:27 by Unknown
In addition to my independent information security assessments through my consultancy Principle Logic, I've been writing a ton...including a lot on Windows 8 and 8.1. Check out these new pieces published by my friends at TechTarget:

What's old, what's new for the enterprise with Windows 8.1

Understanding why Windows 8 for mobile is perfectly viable for enterprise use 

Don’t forget enterprise password protection in a merger or acquisition

Three ways Sysinternals Process Explorer reveals system usage

Ease Windows 8 frustration by focusing on what the OS actually does

Looking at Windows 8 BitLocker full-disk encryption and alternatives

You know the deal...check out principlelogic.com/resources for links to hundreds of additional security resources I've written and developed over the past 12 years.

s always, check out principlelogic.com/resources for links to all of my information security whitepapers, podcasts, webcasts, books, and more. - See more at: http://securityonwheels.blogspot.com/search?updated-max=2013-04-23T21:07:00-04:00#sthash.YSHM1H2R.dpuf
Read More
Posted in bitlocker, Kevin's security content, mobile security, passwords, risk management, security management, security testing tools, windows 8, windows 8.1, Windows Mobile | No comments

Monday, 7 October 2013

Experiencing problems with authenticated web vulnerability scans? Try NTOSpider.

Posted on 11:38 by Unknown
You're performing authenticated web vulnerability scans, right? If you're not, you're missing out...big time.

When performing authenticated scans, you'll find a whole different set of security flaws likely consisting of session fixation, SQL injection (that often differs among user role levels), weak passwords, login mechanism flaws, and perhaps...just maybe that beloved cross-site request forgery flaw that may or may not be exploitable or even matter in the context of what you're doing.

Bottom line: you need to be testing for flaws behind your web login prompts.

The thing is, though, authenticated web vulnerability scanning can extremely painful and inaccurate at best. If you're not paying attention, your web vulnerability scanner is not going to authenticate properly, it's not going to stay logged in, it's going to continually lock the user account (a major annoyance), or it's not going to properly crawl the entire application. Many of these pains are doubly true if your web applications are using Web 2.0 technologies (can we still call them that?).

Web vulnerability scanners are getting better and better, but the problems with authenticated web vulnerability scans still exist with most scanners I've tried - at least some of the time. Except one...NTObjectives' NTOSpider.

I've written about NTOSpider before (here and here) and in the interest of helping out my fellow IT/security professionals who are performing authenticated web vulnerability scans and experiencing these same pains, I feel I have to say something about NTOSpider again...

Check it out. It works extremely well with authenticated scans. Whatever Dan Kuykendall and his guys are doing to get the tool to establish and maintain state - for the entire scan, without locking up, or taking two weeks to run - it's working. Kudos.

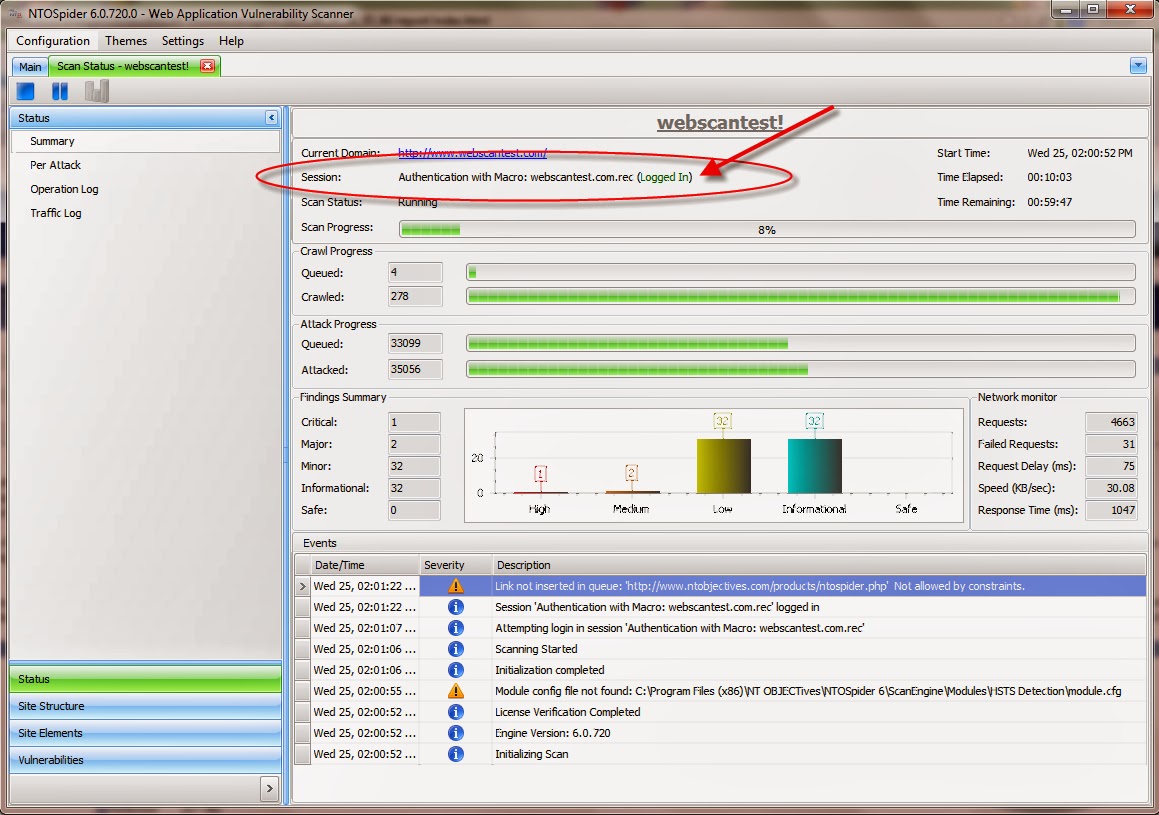
One of the neatest things about NTOSpider is that it will tell you whether or not the scanner is logged in as you can see in the screenshot below:

It's a brilliant feature - something I haven't yet seen on any other web vulnerability scanner. I'm sure some people don't value such a feature (think: "Let's just get this scan done, check our box, and move on!") but it's very useful if you want to make sure your authenticated scans are running properly.

NTOSpider definitely won't find every web security flaw. I haven't yet found a scanner that will. With enough experience, you'll see that this is one of the fundamental problems we have with web vulnerability testing. Relying on a single web vulnerability scanner to find all the flaws is like relying on a single firewall to keep every threat out of your network. It's not going to happen.

NTOSpider is not perfect either. It has several quirks - some of which have been resolved in the latest version 6 (which is much improved). But, again, I haven't yet found a scanner that is perfect.

The only thing that matters is that NTOSpider feels perfect when it ends up getting you out of a bind like it has for me several times now in my web security vulnerability assessment work. Add it to your arsenal of multiple web vulnerability scanners. You won't regret it.
Read More
Posted in cool products, penetration testing, security testing tools, vulnerability assessments, web 2.0, web application security | No comments

Friday, 6 September 2013

Sprechen Sie Deutsch? Hacking For Dummies now in German!

Posted on 11:41 by Unknown
Check out the latest foreign-language edition of my book Hacking For Dummies:


Hacking For Dummies is now in 6 languages: English, Estonian, German, Italian, Portuguese, and Simplified Chinese.Very cool.

If you're like me and English is pretty much your only language, you can see more about that version here.

Prost!

Read More
Posted in hacking, Kevin's books, message from Kevin | No comments

Wednesday, 14 August 2013

Municipal information security weaknesses, hacking, careers, & committees

Posted on 03:31 by Unknown
Here's some new content I've written recently on various information security topics you might be interested in:

Government Security: Uncovering Your Weaknesses (common vulnerabilities I see when performing security assessments for municipalities)

Eight questions to ask yourself before moving to C-suite management (are you really sure you want to do this!?)

IT career paths: Working for yourself is an attainable dream (if you want to stop working for the man)

Top 9 ways to prevent hacking in your enterprise (seriously, you can if you get these basics in check)

How to form a functional enterprise IT security committee (okay, I use the word 'functional' loosely, but it's nowhere but up from here right!?)

In the meantime, check out my website for links to all of my other information security-related content.

Cheers!

Well, in the spirit of my book Hacking For Dummies (be sure to check out the new 4th edition), here are some tips I've written for my friends at TechTarget and Acunetix on some important web and mobile application security issues you need to be tuned in to beyond all the noise that's out there:

Don’t Let Problems Stop You From Carrying Out Web Application Testing  (before 'Too Scared to Scan' was cool ;-)

Mobile app software: Avoid the perpetual cycle of insecurity

Hybrid security: Beyond pen testing and static analysis

Mac Malware Underscores Why You Can’t Ignore Web Security Threats

Do You Scan with Network Security Controls Enabled or Disabled?

Take Care in Handling the Results of Your Web Application Testing

Much more to come on web and mobile security testing...It's what I love doing and I've learned a tremendous amount while doing it over the past decade.

In the meantime, check out my website for links to all of my other information security-related content.


Cheers!
- See more at: http://securityonwheels.blogspot.com/#sthash.tO6G2DOv.dpuf
Read More
Posted in careers, consulting, low-hanging fruit, personal responsibility, security committees, security leadership, thinking long term, vulnerability assessments | No comments

Monday, 12 August 2013

You can't see the light 'til you open your eyes...

Posted on 06:15 by Unknown
I noticed a lot of interesting topics/news coming from the Black Hat conference last week such as:
  •  SSH Communications Security Unveils General Availability Of SSH Risk Assessor Tool
  • Preparing For Possible Future Crypto Attacks
  • Crack of mobile SIM card crypto and virtual machine features could let an attacker target and clone a phone 
  • HTTPS Hackable In 30 Seconds: DHS Alert
No doubt, these are all worthy topics that will help improve information security over the long haul...researched and presented by people who are much smarter than me.

Yet, given where most businesses are with information security today, we've got *much* bigger things to be concerned with such as:
  1. Network shares - open to anyone on the network - providing unfettered access to sensitive information
  2. No proactive event monitoring using the proper tools and expertise (outsource it!)
  3. Firewalls with no passwords or a complex rulebase with a lot of redundancy and risky rules
  4. Phones and tablets with zero security controls
  5. Laptops with no drive encryption (I know most laptops, according to business executives who know more about security than their IT staff, have "nothing of value"...like the ones listed here, but still)
  6. Database servers without passwords, or with default passwords, serving up PII and more to anyone with simple curiosity and a copy of SQL Server Management Studio or Heidi SQL.
  7. Physical security access control and IP video systems that are accessible to anyone on the LAN (sometimes even Wi-Fi) for track covering, system disabling, video deletione, tc.
  8. Operating systems with patch management software that are *still* missing critical updates that are exploitable using free tools to provide full admin access to the system without the attacker ever having to "log in"
  9. Web apps with SQL injection, rampant cross-site scripting, and login mechanisms that are easily manipulated
  10. Mobile apps that have yet to see an iota of security testing
These are all things I find on a consistent basis...Not because I'm smart but because they're very predictable and often go ignored.

"Can't see the light 'til you open your eyes" ...minimal yet insightful lyrics from one of my favorite bands, Black Country Communion. The "light" that people aren't seeing because they're being distracted by flashy headlines, sky is falling "exploits", valueless auditor mandates, or IT execs who are (ironically) "threatened" by information security is the very light that's going to end up biting them if they're not careful...such as the items listed above.

I read something recently from sales/achievement expert Jeffrey Gitomer that said "People who are cocky and arrogant say, I know that and move along. People who are confident and positive ask themselves How good am I at that? and seek to improve."

Great tie-in to the point I'm making. Which side are you on?

Concentrate on the fundamentals and nothing else for now and as long as it takes to ensure you have true control over the information security basics that have been around for decades. Otherwise, you're ignoring the obvious that will rear its head at some point. As we see time again in the research studies (Verizon DBIR, etc.), odds are much greater that you'll get bitten by something silly rather than a niche exploit that hits a relative few.

Finding and fixing the low-hanging fruit (the 20% of vulnerabilities that cause 80% of the problems) is something I've been advising for years and I'm going to keep doing it because that is where the risk is.
Read More
Posted in back to basics, compliance, incident response, low-hanging fruit, scary stuff, security leadership, stupid security, thinking long term | No comments

Thursday, 18 July 2013

Authenticated vulnerability scan pains...Rapid7 to the rescue.

Posted on 08:22 by Unknown
Apparently the folks at Rapid7 have people working on their Nexpose team that have actually performed security assessments for a living. You see, Nexpose has this seemingly trivial feature that can create a world of difference in the life of a security practitioner - it's part of the Site Configuration (i.e. scan settings) called Test Credentials as seen in the following screenshot:
 
Sanity brought about by people who use their own tools in real-world tests

Yep, with Nexpose you can actually test your login credentials before running authenticated vulnerability scans. Imagine that! The last time I remember seeing this feature was in Harris Corporation's STAT scanner about 10 years ago. Now, granted, I haven't used *every* vulnerability scanner out there but why don't we see this feature more often? Is it that difficult to implement programatically? Am I alone in the quest to work more efficiently?

Please, the common response of "Just because you can login doesn't mean you have the privileges to get the results you need" won't cut it...


It's clear - the payoffs of being able to test login credentials in a vulnerability scanner are huge. Some benefits include:
  • confirmation, in advance (key phrase: in advance), that your authenticated scans will actually run
  • less time spent waiting to see what vulnerabilities lie behind the login prompt (there's a LOT more than meets the eye)
  • no reduction in your available scan count (if you happen to be using a tool that charges on a per-scan basis)
  •  no time spent re-running scans (this can be worth hours of time, hassle, and embarassment)
  •  less cussing

I know...it seems trite and many vendors have shown that they're not interested in making such basic improvements to their scanners. I'm sorry - time is money. Given the all the complexities and pressures associated with performing security testing today, the last thing you need is a tool that actually creates more work.

Nexpose saves the day on this one. Kudos Rapid7. Whoever was responsible for this feature, I want to hug their neck.
Read More
Posted in cool products, security audits, security testing tools, stupid security, thinking long term, vulnerability assessments | No comments

Tuesday, 16 July 2013

Never forget this

Posted on 05:59 by Unknown
Although we strive to get others on our side, here's a good reminder from the late Richard Carlson that applies to IT and information security that we should always keep in mind:

"The sooner we accept the inevitable dilemma of not being able to win the approval of everyone we meet, the easier our lives will become".

Speaking of building your confidence and independence, here are some new articles I've written that can help:

Four steps to become a leader in IT problem-solving

Prioritize your IT tasks and finally conquer your to-do list 

Working in IT? Simple steps to get users on your side

In IT planning, try zero-based thinking

Getting hired in IT: How to stand out

As always, check out my website for links to all of my other information security-related content.
Much more to come on web and mobile security testing...It's what I love doing and I've learned a tremendous amount while doing it over the past decade.

In the meantime, check out my website for links to all of my other information security-related content.


Cheers! - See more at: http://securityonwheels.blogspot.com/#sthash.rbih1iU4.dpuf
Read More
Posted in careers, great quotes, information security quotes, Kevin's security content, politics, security leadership, selling security, thinking long term, time management | No comments

Monday, 15 July 2013

Infosec-related quote that strikes a chord

Posted on 06:43 by Unknown
I always love bringing philosophy, leadership, and personal responsibility into the information security discussion and here's one of the best quotes I've come across that resonates across all industries and businesses large and small:

"To see what is right and not do it is a lack of courage." - Confucius


What can you say to that...?

Let this be the fire within that you use to get (and keep) the right people on your side with security the second half of the year so you can have a stellar 2014.
Read More
Posted in careers, great quotes, information security quotes, personal responsibility, security leadership, thinking long term | No comments

Tuesday, 4 June 2013

The root of every infosec failure is...

Posted on 06:44 by Unknown
Time management expert Alec McKenzie once said what could be the most profound statement ever that applies directly to what we do (or don't do) in information security:

"Errant assumptions lie at the root of every failure."

How's your security program looking today?
Read More
Posted in great quotes, information security quotes, security leadership, stupid security, thinking long term | No comments

Friday, 24 May 2013

Quoted in the Wall Street Journal this week

Posted on 04:57 by Unknown
I was quoted in the Wall Street Journal (Tuesday May 21 edition)...it's a piece written by Gregory Millman talking about how senior executives are often at the root of information security problems. Check it out:

Corporate Security's Weak Link: Click-Happy CEOs 
Top Bosses, Exempt From Companywide Rules, Are More Likely to Take Cyber-Attackers' Bait

As I've written in the past, this is a big problem in businesses both large and small based on what I see in my work:

The BYOD Security Loophole


What to do when the CIO gets in the way of enterprise IT security

Read More
Posted in BYOD, careers, Kevin's interviews, kevin's quotes, Kevin's security content, malware, mobile security, security leadership, stupid security | No comments

Tuesday, 21 May 2013

The next time you're feeling bullied...

Posted on 06:21 by Unknown
Ever have a psychopathic executive (in IT or otherwise) try to force you to do something you simply can't support, railroad you down the wrong path, or attempt to make you feel inferior? You're not alone - I see and hear about this a LOT. There are many people pretending to be leaders who are simply insecure in their jobs so they try to flex their muscle to put up a "strong and capable" facade. Ironically it does just the opposite.

Well, when it happens to you, listen intently (people love that) but keep this bit from Henry Wadsworth Longfellow in mind:

"He that respects himself is safe from others; he wears a coat of mail that none can pierce."


Much of what we do in IT and infosec is merely playing the game of politics. If you understand people and why they act the way they do (it's all based around self esteem), you can simply play along and attain some semblance of peace at work.
Read More
Posted in careers, goal setting, scary stuff, security leadership, stupid security, thinking long term | No comments

Saturday, 18 May 2013

Web security answers are changing - a frustrating, challenging, and humbling journey

Posted on 03:40 by Unknown
In reading one of Brian Tracy's books, Brian discusses a story of Albert Einstein and an exam he gave to his graduate physics class at Princeton University. After the exam, Dr. Einstein was approached by a student who asked: "Dr. Einstein, wasn't that the same exam that you gave to this physics class last year?" Dr. Einstein replied "Yes, it was the same exam as last year." The student then asked "But Dr. Einstein, how could you give the same test two years in a row?" Dr. Einstein replied "Because, in the last year, the answers have changed."

This story illustrates the complexities around web application security: how much it changes, how complex it can be, and, most certainly, how no one has all the answers.

I've been fortunate to have the opportunity to test the security of many websites and web applications over the past decade. It's what I love doing the most in my work because every new site/application is a new experience. Of course, some of the security flaws are the same across the board but every new project brings unique challenges. The enormity of the matter is very humbling.

The things that defined web application security flaws (and fixes) last year may not be true this year. The answers are continually changing. Given these factors, I wanted to share with you some of my recent experiences and ideas on how you can get a better grip on this ever-changing target:

Your Scanning Experience Determines Your Scanning Success

What can Developers do to Better Protect PII?

Finding Web Flaws is not Point and Click

Responding to DoS attacks at the web layer

Should you Test Development, Staging or Production?

Read More
Posted in automated scanner oversights, DoS attacks, Kevin's security content, penetration testing, pii, security testing tools, software development, vulnerability assessments, web application security | No comments

Thursday, 2 May 2013

Is your approach to application security based in reality?

Posted on 08:55 by Unknown
I know I say this a lot here - I've been so busy writing that I've been remiss in posting my actual content. So...I've got some content on web and mobile application security and penetration testing this time around.

You see, there are so many researchers, theories, and academic approaches to web and mobile security that it's simply overwhelming. Much of it doesn't apply to what businesses really need to be addressing anyway. Taking the 80/20 approach, what do you really need to focus on that's going to provide the highest payoffs?

Well, in the spirit of my book Hacking For Dummies (be sure to check out the new 4th edition), here are some tips I've written for my friends at TechTarget and Acunetix on some important web and mobile application security issues you need to be tuned in to beyond all the noise that's out there:

Don’t Let Problems Stop You From Carrying Out Web Application Testing  (before 'Too Scared to Scan' was cool ;-)

Mobile app software: Avoid the perpetual cycle of insecurity

Hybrid security: Beyond pen testing and static analysis

Mac Malware Underscores Why You Can’t Ignore Web Security Threats

Do You Scan with Network Security Controls Enabled or Disabled?

Take Care in Handling the Results of Your Web Application Testing

Much more to come on web and mobile security testing...It's what I love doing and I've learned a tremendous amount while doing it over the past decade.

In the meantime, check out my website for links to all of my other information security-related content.


Cheers!


Read More
Posted in Kevin's security content, mobile apps, mobile security, penetration testing, security assessments, security testing tools, source code, source code analysis, vulnerability assessments, web application security | No comments

Friday, 26 April 2013

Clueless in the cloud - think before you act

Posted on 08:30 by Unknown
A recent Network World piece about an RSA 2013 panel that covered cloud forensics and whether or not your cloud providers will be able to come through for you in the event of a lawsuit or breach bringing some critical pitfalls of cloud computing. 

Two things are certain:
  1. If you're lucky enough for your business to be around for the long haul, odds are that it'll ultimately be hit with a lawsuit or a breach in some capacity, some way, that will involve a cloud provider. And...
  2. Your cloud providers won't be prepared to help you out. At least in the foreseeable future.
In an era where cloud providers still believe "security" is a SSAE 16 checkbox, we've got a looong way to go before they're going to be in a position to help us in even greater capacities such as these. They simply don't have the means nor the incentive.

I can't stress this enough: unless you want to appear foolish, think through the security, legal, and business aspects of cloud computing before you fall for the marketing hype and jump on the bandwagon.

I've written pieces with more insight and prescriptive cloud advice here. Take it slow and good luck.

Read More
Posted in cloud computing, compliance, legal, scary stuff, security assessments, stupid security | No comments

Tuesday, 23 April 2013

Wednesday (early) morning's webcast: State of Cyber Security 2013

Posted on 18:07 by Unknown
ISACA and TechTarget are putting it on...It starts tomorrow (Wednesday) morning at 7:45am ET.

Several thousand people will be in attendance...it's the largest crowd I've ever spoken to.

It'll be engaging. It'll be informative. You'll hear what I really think about Obama's Cybersecurity mandates.

You can't miss it.

I'll be kicking things off with the keynote...then I'll be followed by some true information security experts:
  • Theresa M. Grafenstine, Inspector General U.S. House of Representatives
  • Dr. Ron Ross, senior computer scientist and information security researcher, National Institute of Standards and Technology (NIST)
  • Jack E. Gold, founder and principal analyst at J.Gold Associates
and...
  • Chenxi Wang, former vice president, principal analyst serving, Forrester Research Inc.
This is going to be good...I promise. And you can join in the live Q&A to ask me a question, throw me some curve balls, perhaps even send some heckles my way.

Would love to see you there. You can register here. 

Thanks a ton for Kara Gattine, Rachel Shuster, Chris Bent, and all the other fine folks at TechTarget for making this happen.
Read More
Posted in cybersecurity bill, Kevin's keynotes, Kevin's security content, webcasts | No comments

Saturday, 6 April 2013

Must-have Thunderbird to Outlook conversion tool

Posted on 11:37 by Unknown
I recently decided to convert my Thunderbird email to Outlook and didn't have a lot of luck finding a tool that actually worked. Maybe it's because I have a pretty complex Thunderbird configuration with emails dating back to my first messages I sent/received using Netscape Mail (remember that from the 1990s?) .

I came across a tool that was a perfect fit what I needed: Aid4Mail Professional by Fookes Software. It seemed too good to be true but it actually worked! Aid4Mail was relatively quick and I ended up with a .pst file that I could use in Outlook. What I appreciated just as much as the software was the service. I ended up needing some extra help and Julian was very prompt in his replies.

If you're going to buy it, pay the $20 extra and get the 1-year license rather than the 1-time use license. My decision to purchase the latter was part of why I had to bug Julian several times but he ended up geting me out of the bind I was in. I'm probably going to need to acquire another license (1 year this time!) because I still have some work to do but at least I now know what tool to use for this purpose.

Definitely a tool worth checking out if you're one of the prideful few like myself who is still using Thunderbird or any of the other old-school email clients that Aid4Mail supports (i.e. Windows Mail, Apple Mail, Eudora, Pegasus, etc).


Read More
Posted in cool products | No comments
Newer Posts Older Posts Home
Subscribe to: Posts (Atom)

Popular Posts

  • Reaver Pro: a simple tool for cracking WPA on a LOT of wireless networks
    If wireless security testing is on your radar, you need to get Reaver Pro . As I outlined in this Hacking For Dummies, 4th edition chapter ,...
  • Low information users and the challenges they create
    Thanks to the political elite and the dumb masses they inspire, you've probably heard the term low information voter …In a nutshell, thi...
  • "Top Blogs" list & some home security considerations
    I think I may have found the first sign that my blog is growing and gaining some traction. I've made it to the Top 20 Home Security Blog...
  • Wooo...HIPAA audits are coming & the irony of KPMG's involvement
    I've always believed that compliance is a threat to business [hence why I help businesses take the pain out of compliance by addressing ...
  • Windows 8.1 changes/enhancements, BitLocker's improvements, and related Windows mobile/security tips
    In addition to my independent information security assessments through my consultancy Principle Logic , I've been writing a ton...includ...
  • What you need to know about security vulnerability assessments (that no one is willing to share)
    I'd love it if you'd join me over at SearchSecurity.com next week where I'll be talking about the rest of the story regarding ...
  • Sprechen Sie Deutsch? Hacking For Dummies now in German!
    Check out the latest foreign-language edition of my book Hacking For Dummies: Hacking For Dummies is now in 6 languages: English, Estonian, ...
  • It's hard being human
    Cavett Robert once said something about character that resonates within information security - especially regarding ongoing management and l...
  • Experiencing problems with authenticated web vulnerability scans? Try NTOSpider.
    You're performing authenticated web vulnerability scans , right? If you're not, you're missing out...big time. When performing a...
  • The compliance crutch mentality rides on
    I believe it was my colleague Kevin Bocek who once said: "Security done right will yield compliance for free. Compliance for complianc...

Categories

  • active directory
  • application firewalls
  • APTs
  • aslr
  • atm security
  • audio programs
  • audit logging
  • automated scanner oversights
  • back to basics
  • backups
  • big brother
  • bitlocker
  • budget
  • business case for security
  • business continuity
  • BYOD
  • car hacking
  • careers
  • certifications
  • change management
  • checklist audits
  • cissp
  • clear wireless
  • cloud computing
  • communication
  • compliance
  • computer glitch
  • conferences
  • consulting
  • content filtering
  • cool products
  • cool sites
  • cross-site request forgery
  • cross-site scripting
  • csrf
  • customer no service
  • cybersecurity bill
  • data at rest
  • data breach laws
  • data breaches
  • data centers
  • data destruction
  • data leakage
  • data protection
  • data retention
  • database security
  • degrees
  • desktop management
  • disaster recovery
  • disk imaging
  • disposal
  • dns
  • document security
  • domino
  • DoS attacks
  • drive encryption
  • e-discovery
  • ediscovery
  • employee monitoring
  • encrypting data in transit
  • encryption
  • end point security
  • ethical hacking
  • exchange
  • experience
  • expert witness
  • exploits
  • facebook
  • FERPA
  • file integrity monitoring
  • firewalls
  • forensics
  • full disk encryption
  • global warming
  • goal setting
  • good blogs
  • government intrusion
  • government regulations
  • great quotes
  • hacking
  • hardware
  • hipaa
  • hitech
  • hitech act
  • home security
  • humor
  • identity access management
  • identity theft
  • IIS
  • incident response
  • information classification
  • information security quotes
  • intel
  • intellectual property
  • internal threat
  • java
  • Kevin's books
  • Kevin's interviews
  • Kevin's keynotes
  • kevin's panels
  • kevin's quotes
  • Kevin's security content
  • Kevin's seminars
  • Kevin's videos
  • laptop encryption
  • laptop security
  • legal
  • Linux
  • locking screens
  • low-hanging fruit
  • malware
  • marketing hype
  • message from Kevin
  • messaging security
  • metasploit
  • metrics
  • mobile apps
  • mobile security
  • motivation
  • multi-factor authentication
  • network analysis
  • network complexities
  • network protocols
  • network security
  • networking essentials
  • Novell
  • office
  • online backup
  • online safety
  • open source security
  • owasp
  • p2p
  • passwords
  • patch management
  • patching
  • pci 6.6
  • pci dss
  • PCNAA
  • penetration testing
  • people problems
  • personal responsibility
  • phishing
  • physical security
  • pii
  • podcasts
  • policy enforcement
  • politics
  • presentations
  • privacy
  • quality assurance
  • recommended books
  • recommended magazines
  • recycling
  • remote access security
  • ridiculous password requirements
  • risk analysis
  • risk management
  • rogue insiders
  • ROI
  • RSA 2012
  • running a business
  • saas
  • salary
  • scary stuff
  • sccm
  • sdlc
  • security assessments
  • security audits
  • security awareness
  • security committees
  • security leadership
  • security management
  • security operations
  • security policies
  • security policy
  • security scans
  • security standards
  • security statistics
  • security technologies
  • security testing tools
  • security tools
  • selling security
  • sharepoint
  • small business
  • smartphone security
  • SMBs
  • social media
  • software development
  • source code
  • source code analysis
  • special offer
  • SQL injection
  • sql server
  • ssl
  • storage security
  • student information systems
  • stupid security
  • success
  • telecommuting
  • testimonials
  • thinking long term
  • third-party applications
  • threat modeling
  • time management
  • training
  • twitter
  • uncool products
  • unstructured information
  • unstructured infromation
  • user awareness
  • vendors
  • virtual machine security
  • visibility
  • voip
  • vulnerability assessments
  • web 2.0
  • web application security
  • web browser security
  • web server security
  • webcasts
  • WebInspect
  • whitelisting
  • whitepapers
  • Windows
  • Windows 7
  • windows 8
  • windows 8.1
  • Windows Mobile
  • windows security
  • Windows Vista
  • wireless
  • wireless security
  • zero tolerance

Blog Archive

  • ▼  2013 (35)
    • ▼  November (3)
      • Reaver Pro: a simple tool for cracking WPA on a LO...
      • Low information users and the challenges they create
      • My latest security content (lots of stuff on appli...
    • ►  October (3)
    • ►  September (1)
    • ►  August (2)
    • ►  July (3)
    • ►  June (1)
    • ►  May (4)
    • ►  April (4)
    • ►  March (4)
    • ►  February (5)
    • ►  January (5)
  • ►  2012 (77)
    • ►  December (2)
    • ►  November (2)
    • ►  October (4)
    • ►  September (3)
    • ►  August (3)
    • ►  July (4)
    • ►  June (5)
    • ►  May (9)
    • ►  April (5)
    • ►  March (10)
    • ►  February (14)
    • ►  January (16)
  • ►  2011 (163)
    • ►  December (15)
    • ►  November (11)
    • ►  October (9)
    • ►  September (16)
    • ►  August (13)
    • ►  July (8)
    • ►  June (13)
    • ►  May (18)
    • ►  April (16)
    • ►  March (13)
    • ►  February (13)
    • ►  January (18)
  • ►  2010 (170)
    • ►  December (10)
    • ►  November (14)
    • ►  October (7)
    • ►  September (27)
    • ►  August (20)
    • ►  July (8)
    • ►  June (15)
    • ►  May (4)
    • ►  April (23)
    • ►  March (21)
    • ►  February (11)
    • ►  January (10)
  • ►  2009 (55)
    • ►  December (5)
    • ►  November (10)
    • ►  October (21)
    • ►  September (19)
Powered by Blogger.

About Me

Unknown
View my complete profile